The 2026 LiteLLM Supply Chain Breach: A Deep Dive into the Impact and Ethical Disclosure
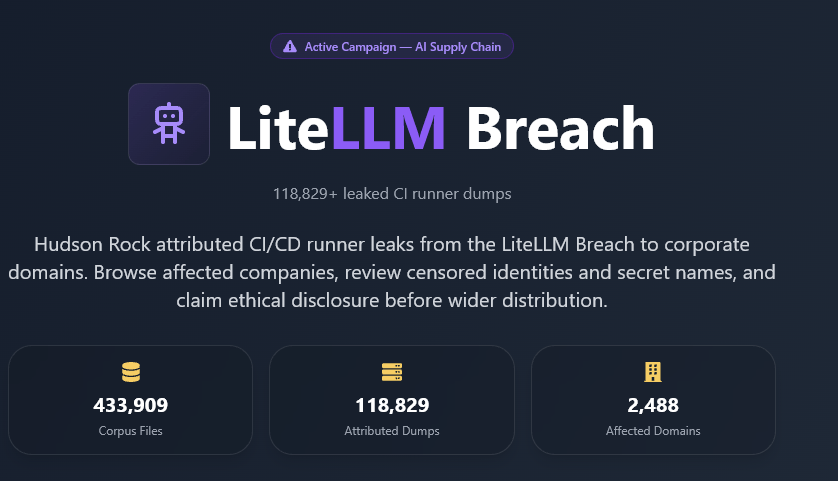
The cybersecurity world is abuzz with the news of a massive supply chain breach involving LiteLLM, a widely-used open-source AI proxy gateway. This attack, orchestrated by the threat actor group TeamPCP, has compromised the CI/CD pipelines of thousands of global enterprises, leading to the exfiltration of sensitive data and secrets. The sheer scale of this breach is staggering, with a 153GB raw database containing 433,909 files and 118,829 CI runner dumps attributed to 2,488 affected corporate domains.
What makes this breach particularly insidious is the lack of clear organizational attribution in many of the leaked files. While some CI/CD pipelines are configured generically, many contain active database passwords, third-party API keys, and cloud credentials without any identifiable company email, custom domain string, or internal server name. This means countless organizations are currently unaware of their exposure.
The impact of this breach is far-reaching, affecting some of the world's most prominent companies, including Amazon Web Services (AWS), Samsung Electronics, Cisco Systems, Salesforce, ServiceNow, S&P Global, Siemens AG, John Deere, Deloitte, Epic Games, Orange S.A., TomTom, and BT Group. The breach has been so significant that Hudson Rock, the cybersecurity firm behind the discovery, has launched a dedicated portal for affected organizations to verify their impact and receive ethical disclosures.
The attack mechanics are complex, involving the compromise of the GitHub Actions pipeline for Trivy, a popular open-source vulnerability scanner. The poisoned security scanner was granted legitimate read access to the LiteLLM developers' runner environment, allowing the attackers to exfiltrate LiteLLM's PyPI publishing tokens. Armed with these credentials, TeamPCP published malicious versions of the package (1.82.7 and 1.82.8), which executed a three-stage payload harvesting environment variables, local configuration files, and attempting lateral movement across Kubernetes clusters.
The payload delivery was stealthy, utilizing a .pth Python startup hook that executed the moment the Python interpreter initialized, regardless of whether the LiteLLM library was explicitly imported. This allowed the threat actors to harvest live environment memory and configurations mid-execution, installing a persistent systemd backdoor.
The attribution challenge is significant, as accurate attribution requires looking beyond the surface-level committer emails to analyze the actual infrastructure boundaries. For example, in one high-profile compromise, the committer email associated with the pipeline run belonged to @siriusxm.com, but further examination of the environment dump revealed that the breach occurred within the infrastructure of AdsWizz, a subsidiary of SiriusXM.
The ethical disclosure process is crucial, as affected organizations can verify their impact through Hudson Rock's look-up tool and receive access to view their specific leaked data within the Cavalier threat intelligence platform. Immediate remediation guidance includes aggressive credential revocation, audit logging, and egress filtering, as well as inspecting for persistence in local development environments and containers.
In conclusion, the 2026 LiteLLM supply chain breach is a stark reminder of the vulnerabilities in the AI supply chain. The attack's scale, stealth, and impact on global enterprises highlight the need for robust cybersecurity measures and ethical disclosure processes to protect sensitive data and prevent further damage.